• Link to Rss this site
  • Link to LinkedIn
  • Link to Youtube
  • Link to Instagram
  • English English English en
  • Deutsch Deutsch German de
Sales: +49 5251 390969-180 | Support: +49 5251 390969-300
NoSpamProxy
  • PRODUCTS
    • Platforms
      • NoSpamProxy Cloud
      • NoSpamProxy Server
      • NoSpamProxy 25Reports
  • SOLUTIONS
    • Threat Protection
      • Protection against Spam, Phishing & Malware
      • AI Threat Detection
      • Isolated File Analysis
      • Microsoft 365 Mail Security
    • Secure Email Communication
      • Email Encryption
      • Automatic Certificate Management
      • Search for Public Keys
    • Productivity & Compliance
      • Sending Large Files
      • Email Disclaimer
  • INDUSTRIES
    • By Company Size
      • Large Companies
      • Small and Medium-Sized Enterprises
    • Regulated Industries
      • Public Institutions
      • Healthcare
      • Finance
      • Law
    • Success Stories
      • Testimonials
      • Awards
  • PARTNERS
    • Resellers
      • Finding Resellers
      • Become a Reseller
      • Become an MSP Partner
    • For Existing Partners
      • Partner Portal
      • Partner Trainings
      • NFR Licenses
  • RESOURCES
    • Support
      • Online Documentation
      • Forum
      • Support
    • Continuing Education
      • Training Courses
      • Webcasts
    • Knowledge
      • Blog
      • Newsletter
    • Downloads
      • NoSpamProxy Server
    • Events
      • Events
      • Webcasts
  • PRICING
  • CONTACT
  • FREE TRIAL VERSION
    • Price Request
    • Free Trial Version
  • English
    • Deutsch
  • Click to open the search input field Click to open the search input field Search
  • Menu Menu
  • Emotet nutzt verschlüsselte Archivformate

32Guards News: Emotet Uses Encrypted Archive Formats

The current threat situation is shaped by the trojan Emotet. A striking feature of cyber attacks is that the attack patterns vary rapidly. This makes it difficult to specifically detect Emotet threats at all levels.

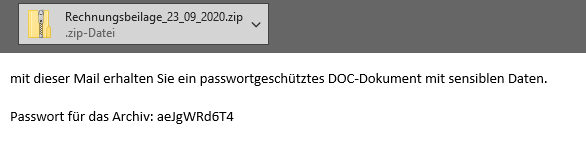
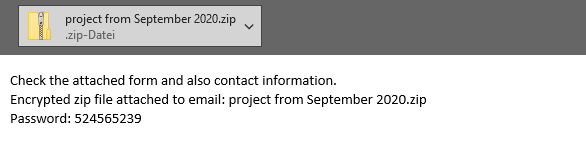
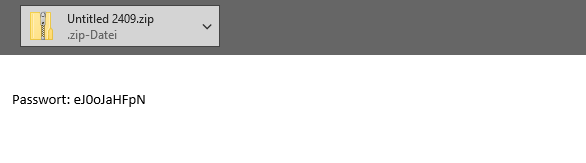
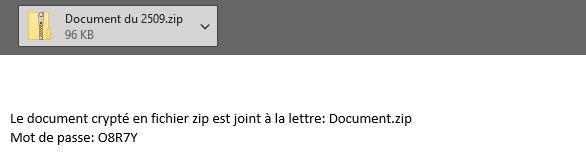
Very often emotet emails are used to distribute emotet Emails that either contain a contaminated Word document with macros or a link to a similar one. Another strategy of the attackers is to hide such corrupted Word files in encrypted archive formats. A central problem here is that classic malware scanners cannot decrypt and automatically examine the archive. To make it as “easy” as possible for the victim of the malware attack, the required password for decryption is included in the text of the Email (see examples). As a side effect, the attackers have the option of simply re-encrypting the same malware over and over again. Due to the constantly changing hash values, simple protection mechanisms can be overridden here.

  • Emotet nutzt verschlüsselte Archivformate
  • Emotet nutzt verschlüsselte Archivformate 2
  • Emotet nutzt verschlüsselte Archivformate 3
  • Emotet nutzt verschlüsselte Archivformate 1
Previous Previous Previous Next Next Next
1234

32Guards’ Watchful Eye

Based on the data collected during the 32Guards project, the NoSpamProxy experts can continuously monitor the threat situation and actively protect customers who are already participating in the 32Guards beta. A look at the sightings of encrypted zip archives provides the first suspicious hints at the threat:
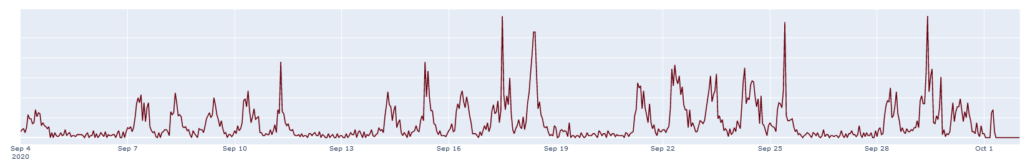
NoSpamProxy-Operation-ZipLock-EncryptedZIPTotal-Last4Weeks

This graph shows the time course of views of encrypted zip archives. Here from 15.9.2020 a clearly increased emergence shows up. This trend becomes even clearer if you look at the attachments of inbound emails not processed by Level of Trust. Basically, it can be observed that a large proportion of malware comes from unknown communication partners. The corresponding time course speaks an even clearer language:
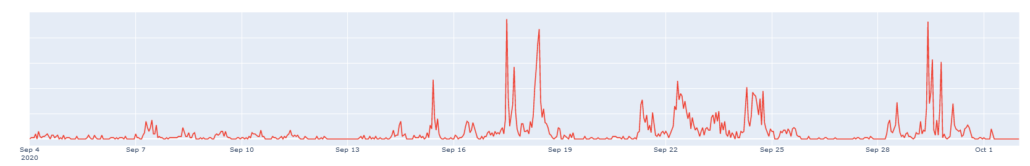
Emotet nutzt verschlüsselte Archivformate Grafik 2

It is obvious that the situation has changed significantly in the last two weeks. A close look at the corresponding metadata reveals a large part of these additional attachments to be suspicious. For example, there are a large number of suspicious file names with words frequently used in malware attacks, such as “IBAN”, “invoice” or “order”. Cryptolaemus also warns on Twitter about encrypted archives in conjunction with Emotet.

About mealybugs and ladybugs

The US company Symantec has established the term “Mealybug” for the actors behind the Trojan Emotet, which translated would be the mealy bug. The natural predators of mealybugs include ladybugs, and in Australia a special type of ladybug (Latin: Cryptolaemus montrouzieri) is bred and marketed. Thus, the name of the unofficial “Emotet Working Group” was born out of a worldwide collective of IT security experts* who together fight the emotet botnet and network via Twitter. The collected IoCs (Indicators of Compromise: daily updated indicators for emotet detection) from the Cryptolaemus team are consumed by 32Guards and are available in the 32Guards beta.

Optimise Existing Protection Through Optimal Configuration

All NoSpamProxy customers currently participating in the 32Guards beta are currently protected by 32Guards’ warnings in many cases. Nevertheless, it is highly recommended to configure the system locally in the best possible way to meet the current situation.

Check Password-Protected Files Carefully

In general, the best practice recommendation for encrypted content is not to deliver it without checking for spam, malware or policy violations. As described above, the danger with encrypted ZIP archives is currently very high due to the Emotet operation “Zip Lock”. Anyone who has not yet thought done so is well advised to define an approach to password-protected files for their company as soon as possible and to implement it accordingly in NoSpamProxy.

Since 2018, we strongly recommend to use a whitelisting approach for content filtering (keyword: Email firewall). Customers who have already implemented this may not need to take any action at all; this was not previously required in the workflow in the respective companies, for example when files were securely shared via the cloud or NoSpamProxy Larges Files.

Configuring content filters correctly

Since NoSpamProxy Version 13.1, the file type “Encrypted ZIP-compressed file” is explicitly available in the content filter. So it is possible to block these files first and upload them to the Web Portal. Only after manual approval by the administrator does the relevant attachment become available to the end user. Of course, it is also possible to create content filter entries that can differentiate between emails without trust (such as the current spam wave) and those from regular communication partners (which have been identified accordingly by Level of Trust).

Use 32Guards Now

The 32Guards action in NoSpamProxy collects and analyses metadata about emails and attachments. The goal: to build an even more powerful anti-malware intelligence that can detect and fend off attacks by spam and malware even faster and more purposefully. If you are interested in using the beta version of 32Guards, send an email with the subject “32Guards activation” to NoSpamProxy support and attach a screenshot of your license details.

Use 32Guards now
  • share 
  • share 
  • share 
  • email 

SEARCH

PRODUCT

  • All Topics
  • NoSpamProxy Cloud
  • NoSpamProxy Protection
  • NoSpamProxy Encryption
  • NospamProxy Large Files

NoSpamProxy Newsletter

Subscribe to Newsletter

You need support?

You can find more information about NoSpamProxy in our documentation and forum.

CATEGORY

  • All Topics
  • News
  • News
  • Product
  • Product
  • Tech & Support
  • Tech & Support
  • Events
  • Events
Net at Work GmbH
Am Hoppenhof 32 A
33104 Paderborn
Tel. +49 5251 390969-000
Fax +49 5251 390969-009
www.nospamproxy.com
RSS Feed Logo RSS Feed Logo Subscribeto RSS Feed

NoSpamProxy

  • About us
  • Career
  • General terms and conditions
  • Data Protection Information for Business Partners and Applicants
  • Cybersecurity (PSIRT)

Partners

  • Finding resellers
  • Becoming a reseller
  • Becoming a MSP Partner
  • Newsletter Subscription
  • Order Certificates

Categories

  • All topics
  • News
  • Support
  • Product
  • Events
  • Updates

Latest News

  • NoSpamProxy Info Icon
    NoSpamProxy continues to evolve: greater focus on product and partner business01.09.2026 - 10:00
  • Info Icon
    Action Required: Renew Permissions for the Entra ID User Import14.08.2026 - 13:59
  • info icon
    NoSpamProxy and TLS Certificates: What Will Change by 202907.08.2026 - 10:00
IMPRINT • EULA • Privacy Policy • • © 2026 Net at Work GmbH
  • Link to Rss this site
  • Link to LinkedIn
  • Link to Youtube
  • Link to Instagram
Link to: (Almost) All roads lead to the cloud Link to: (Almost) All roads lead to the cloud (Almost) All roads lead to the cloud(Fast) alle Wege führen in die Cloud Preview Link to: Cloud solution is the focus of the Security Insider Deep Dive Link to: Cloud solution is the focus of the Security Insider Deep Dive NoSpamProxy im Security Insider Deep Dive PreviewCloud solution is the focus of the Security Insider Deep Dive
Scroll to top Scroll to top Scroll to top